Configured targets
Choose apps you want XAIPT to observe and protect. Target identity and enforcement health matter; selection alone is not a Protected claim.
XAIPT Guard is a protection layer for configured Android app access. When a protected target opens, XAIPT can hold the boundary, require fresh authority, grant bounded access, and relock—while Recovery, Vault and evidence remain separate, understandable product surfaces.
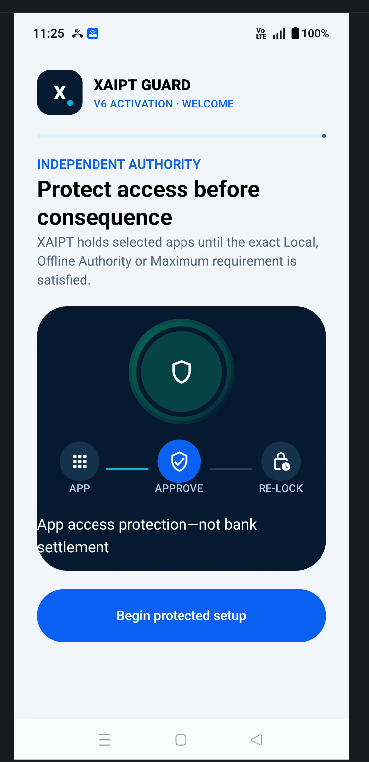
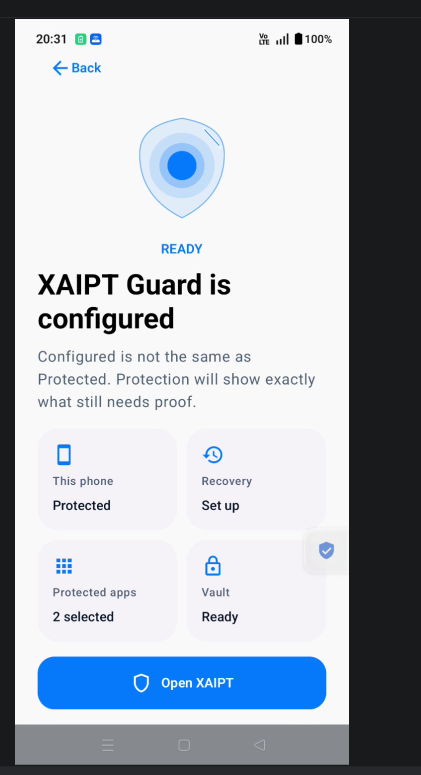
XAIPT is designed around Authority Before Action and bounded consequence. The visible interface follows the same security truth as the runtime underneath it.
Choose apps you want XAIPT to observe and protect. Target identity and enforcement health matter; selection alone is not a Protected claim.
A held access request requires the admitted authority path. The current local path uses fresh strong biometric-backed approval rather than a durable “already authenticated” flag.
Recovery packages, authority succession and verification remain a separate domain. Recovery does not silently become access approval.
The product meaning is simple enough to understand at a glance, while the security contract stays strict underneath.
XAIPT’s protection center brings target selection, enforcement readiness, authority requirements and proof status together. It is designed to show what is configured, what is ready, and what still needs proof—without decorative “security percentages.”
Vault is a separate protected content surface. It does not claim to secure arbitrary third-party data.
Security events are projected as understandable activity—not raw developer logs or fabricated confidence scores.
Create, preserve and verify a Recovery Package, then use controlled succession when authority must be replaced.
A premium security product earns trust by separating implemented behavior from architecture that has not yet been admitted for public use.
XAIPT is not presented as “AI everything.” Each product keeps a clear job and boundary.
XAIPT Guard focuses on protected access, bounded authority, continuity and recovery. Its mission is PROTECT → SURVIVE → RECOVER.
XMECK is the separate private/offline-first intelligence product direction: local and governed model workflows, projects, knowledge and agents. XAIPT remains the protection product; XMECK remains the intelligence product.
The website is prepared to become the public policy/support surface, but Play publication remains correctly blocked until the qualified Android artifact and declarations match reality.
XAIPT Guard is moving through controlled physical and release qualification. Public download should activate only when the qualified build, Play declarations and published policies describe the same product.